
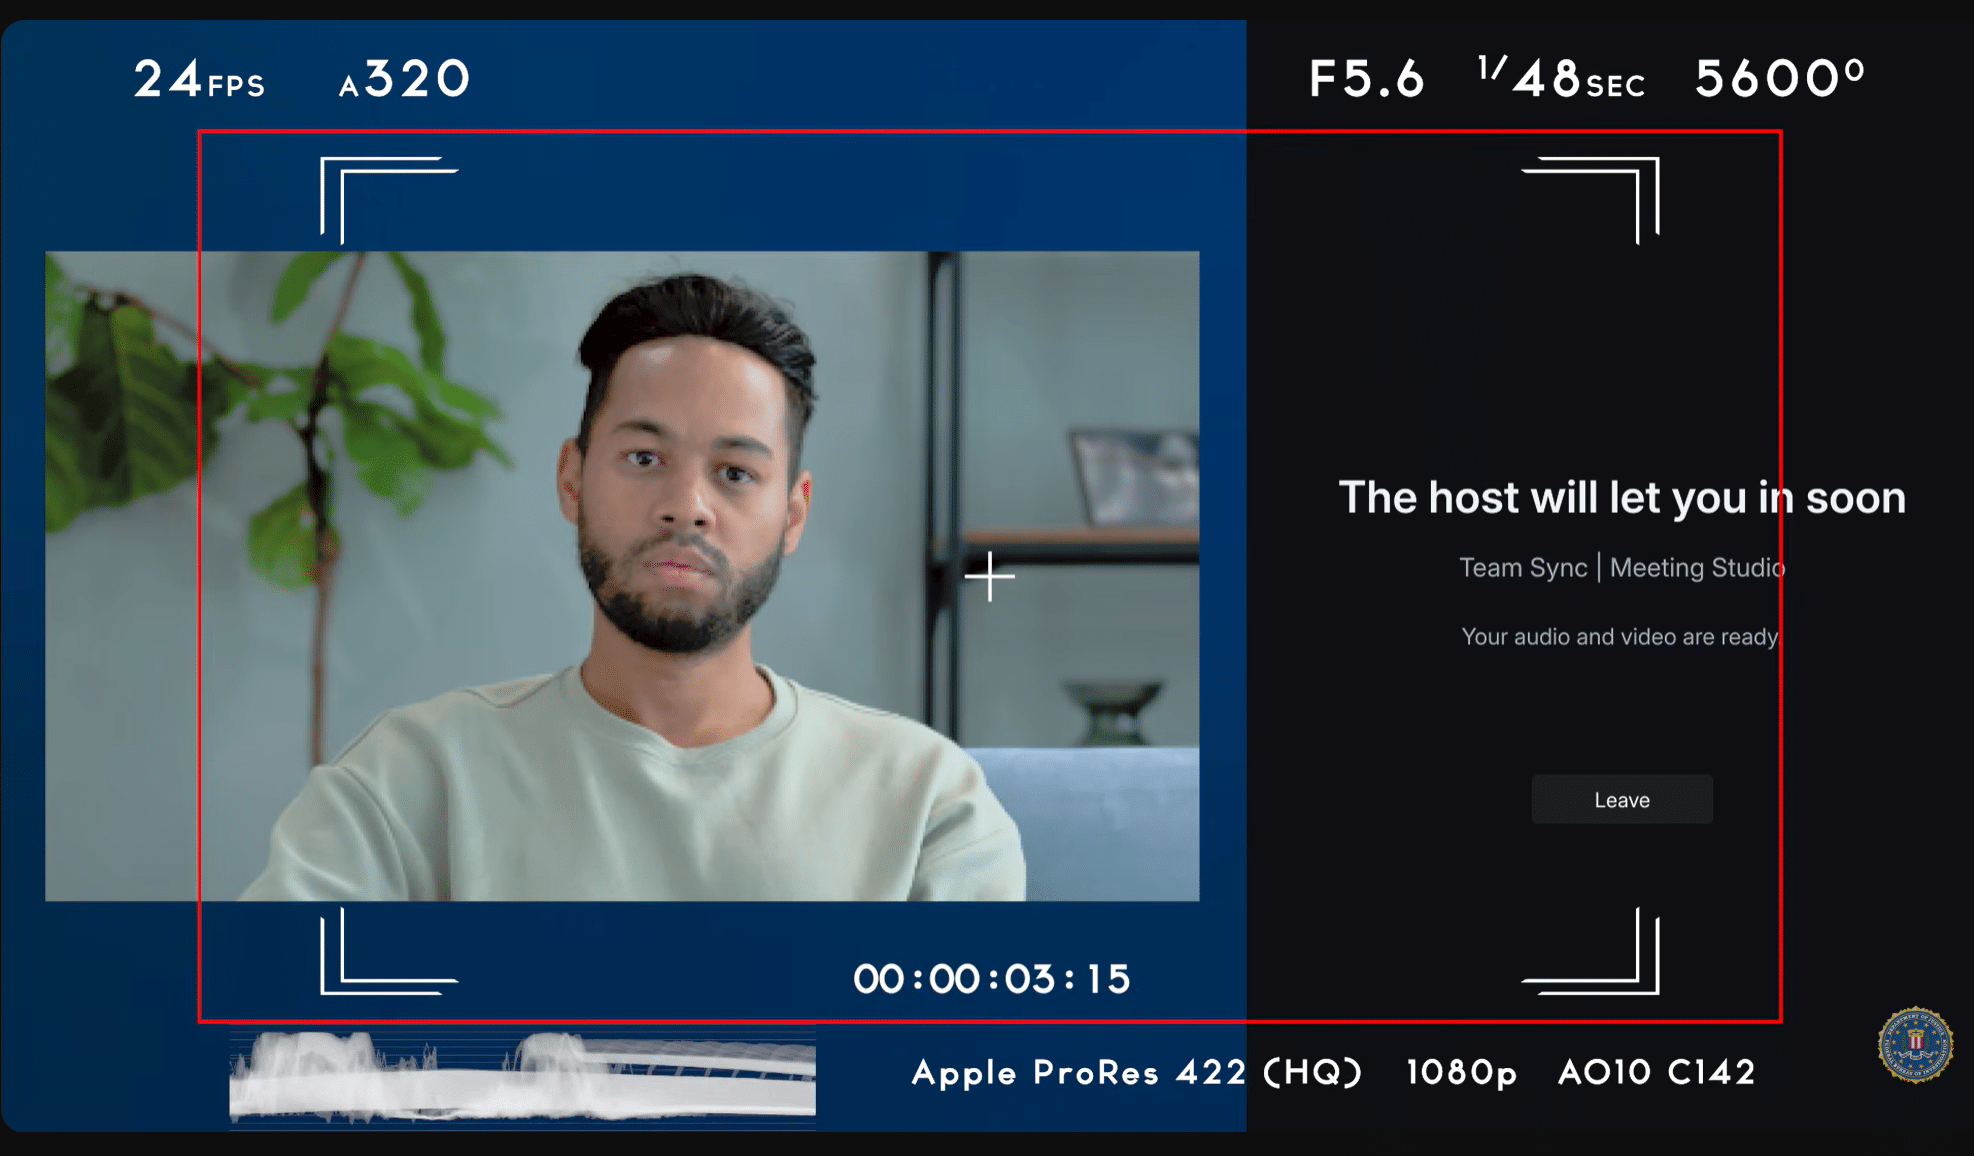
FaceStealer typically begins with a compromised individual whose communications accounts, contact lists, conversation histories, and webcam recordings have been stolen. Using that person’s legitimate Telegram account or another hijacked platform, the hackers invite contacts to what appears to be a routine Zoom or Microsoft Teams meeting. Because the attackers possess previous messages, invitations can reference established business relationships. Legitimate scheduling services such as Calendly add credibility. Shortly before the meeting, the target receives a link that looks like a legitimate conferencing address but leads to an attacker-controlled replica. Once the target joins, hackers play prerecorded footage of the person whose account was compromised. Several recorded participants may appear simultaneously, creating the impression of an ordinary group meeting. The attackers then manufacture a technical problem, often claiming the target’s microphone is malfunctioning. A supposed participant offers instructions to repair it by installing an update, executing a script, or entering commands into a computer terminal. Those instructions install malware that can harvest browser cookies, record keystrokes, capture screens, and establish persistent access. Meanwhile, the counterfeit meeting has already begun recording the new victim’s webcam.
Source: www.biometricupdate.com